Heavy Shadow AI Use Adds About $670K to the Average Breach. Do You Know Where Your Business Is Exposed?
Start your AI Amnesty today. The free checklist shows which AI tools your team is using, which ones put data at risk, and what to fix first, in 15 minutes.
Source: IBM Cost of a Data Breach Report 2026.
20+ YEARS
RISK MANAGEMENT · CPA · CFA
ISO 42001
AI GOVERNANCE FRAMEWORKS
NIST & EU AI ACT
COMPLIANCE EXPERTISE
Here’s What’s Inside the Checklist
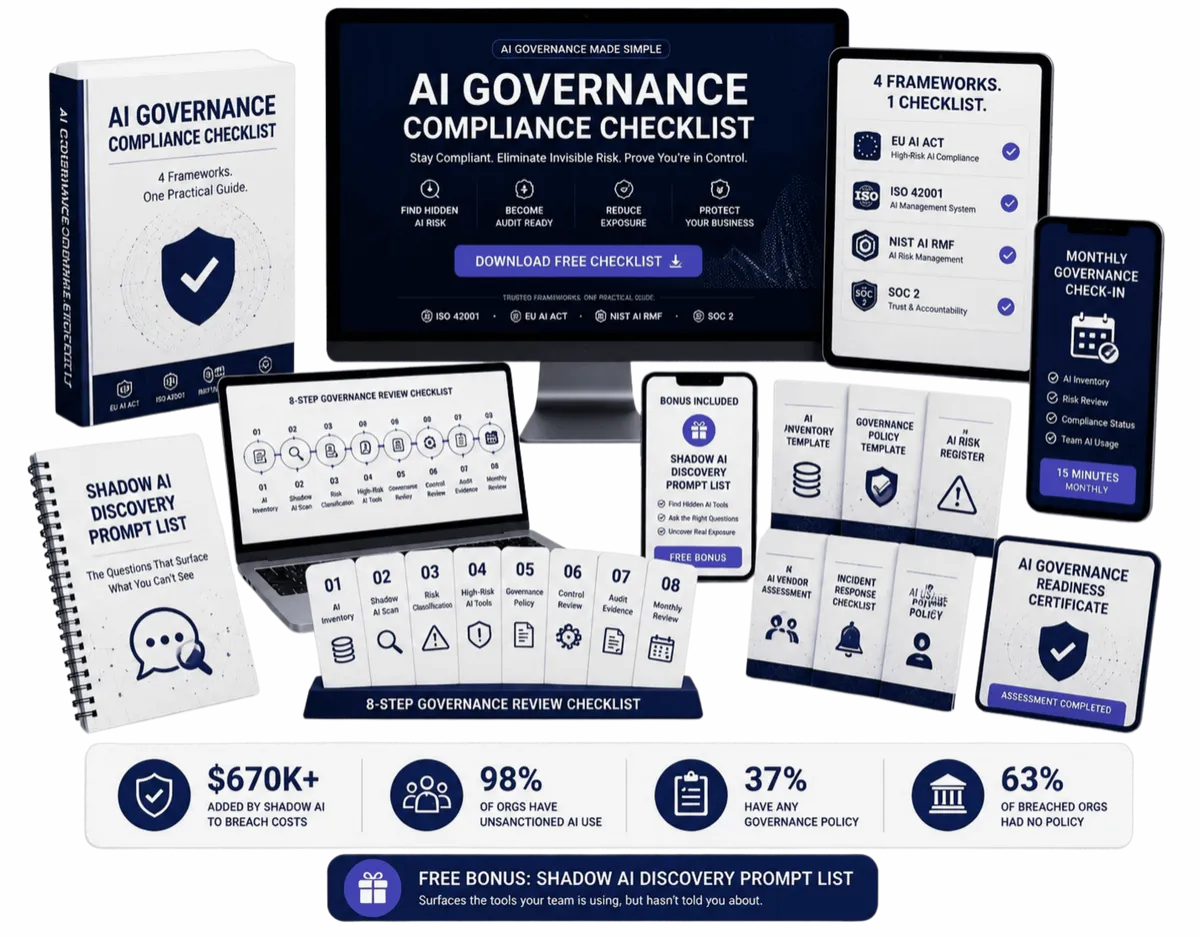
Identify Your Shadow AI Exposure Discuss where unapproved AI tools may be operating inside your organization and the potential risks to sensitive business data.
Understand Your Compliance Gaps Explore how your current AI practices align with ISO 42001, NIST AI RMF, and applicable EU AI Act requirements.
Review Your Existing AI Governance Discuss your current AI policies, risk assessments, vendor oversight, and internal accountability.
Prioritize Your Biggest Risks Identify the governance areas that deserve immediate attention and where stronger controls may be needed.
Build a Clear Path Forward Understand the practical next steps toward better AI visibility, accountability, and governance.
YOUR AI GOVERNANCE EXPERT
AFTAB SABIR
Aftab Sabir is a TEDx speaker and enterprise risk and governance expert with over 20 years of experience managing capital programs, risk frameworks, and governance infrastructure at some of Canada’s largest organizations.
He has built governance systems for multi-billion-dollar infrastructure programs, led cross-functional risk teams, and established best-practice standards across regulated industries.
Aftab founded Fair & Square AI to bring that same rigor to the one area where most mid-market organizations are flying completely blind: AI governance.
Proven Governance Experience at Scale
Aftab has designed and led governance systems across major infrastructure, municipal, and telecommunications programs. His experience demonstrates the same disciplined oversight organizations need to manage AI risk.
National Broadband Risk Governance
Managed governance for high-speed internet programs serving approximately 200,000 underserved premises across more than 100 municipalities under programs valued from $500M to $1B.
Aftab optimized vendor resources by 20% and implemented standardized governance with risk logs, dashboards, and integrated schedules giving executives a clear, compliant view of program health.
Municipal ICFR & PCI Data Governance
Supported governance across $2B in procurement and $30M in corporate card spending by expanding ICFR, building a policy-management tool, and designing risk-based auditing standards.
This standards-based approach reflects the controls organizations need to align AI systems with ISO 42001, NIST AI RMF, and other governance requirements.
Enterprise JIRA Governance for PureFibre
Replaced spreadsheet-driven governance with a centralized enterprise JIRA platform for a Canadian telecommunications program deploying approximately $1B annually.
The system centralized projects, risks, KPIs, and change-management rules, generated 1,000 hours of savings, and created a scalable governance model across multiple business units.
Who This Is Built For
This Is for You If…
You’re a CEO, COO, head of IT, or risk and compliance leader.
Your organization uses AI tools but doesn’t have a formal governance process.
You have an AI policy document but no real visibility into what’s running.
You need a clear, practical starting point you can act on immediately.
This Isn’t For…
Large enterprise teams with dedicated compliance departments.
Organizations with established platform budgets for AI governance.
Anyone looking for a replacement for legal or regulatory advice.
1 in 4
malicious breaches are now AI-enabled, up 56% year on year
IBM, COST OF A DATA BREACH
2026
$6M
average cost of an AI-enabled breach, against $4.99M for all breaches
IBM, COST OF A DATA BREACH
2026
43%
of breached organizations had shadow AI in play, up from 20%
IBM, COST OF A DATA BREACH
2026
247 days
mean time to identify and contain, the first rise in five years
IBM, COST OF A DATA BREACH
2026
DOWNLOAD IT. RUN THROUGH IT. THEN YOU’LL KNOW EXACTLY WHERE YOU STAND.
The checklist will tell you exactly what you’re supposed to have in place and where the gaps are most likely hiding in your organization.
You don’t need a compliance team or a platform subscription to use it just 15 minutes and the willingness to look honestly at what’s actually running.
© 2026 Fair & Square AI. All rights reserved.
Privacy Policy | Terms & Conditions | Contact
Practical AI governance for organizations that need greater visibility, stronger compliance, and less risk. By entering your details, you agree to receive emails from Fair & Square AI. You can unsubscribe at any time. We respect your privacy and will never share your information. Results depend on individual circumstances. The information provided is for educational purposes only and does not constitute legal or regulatory advice.